Call Recording Retention Guide for Enterprises
A call recording retention guide for setting defensible policies, securing sensitive recordings, and reducing storage costs without sacrificing control.
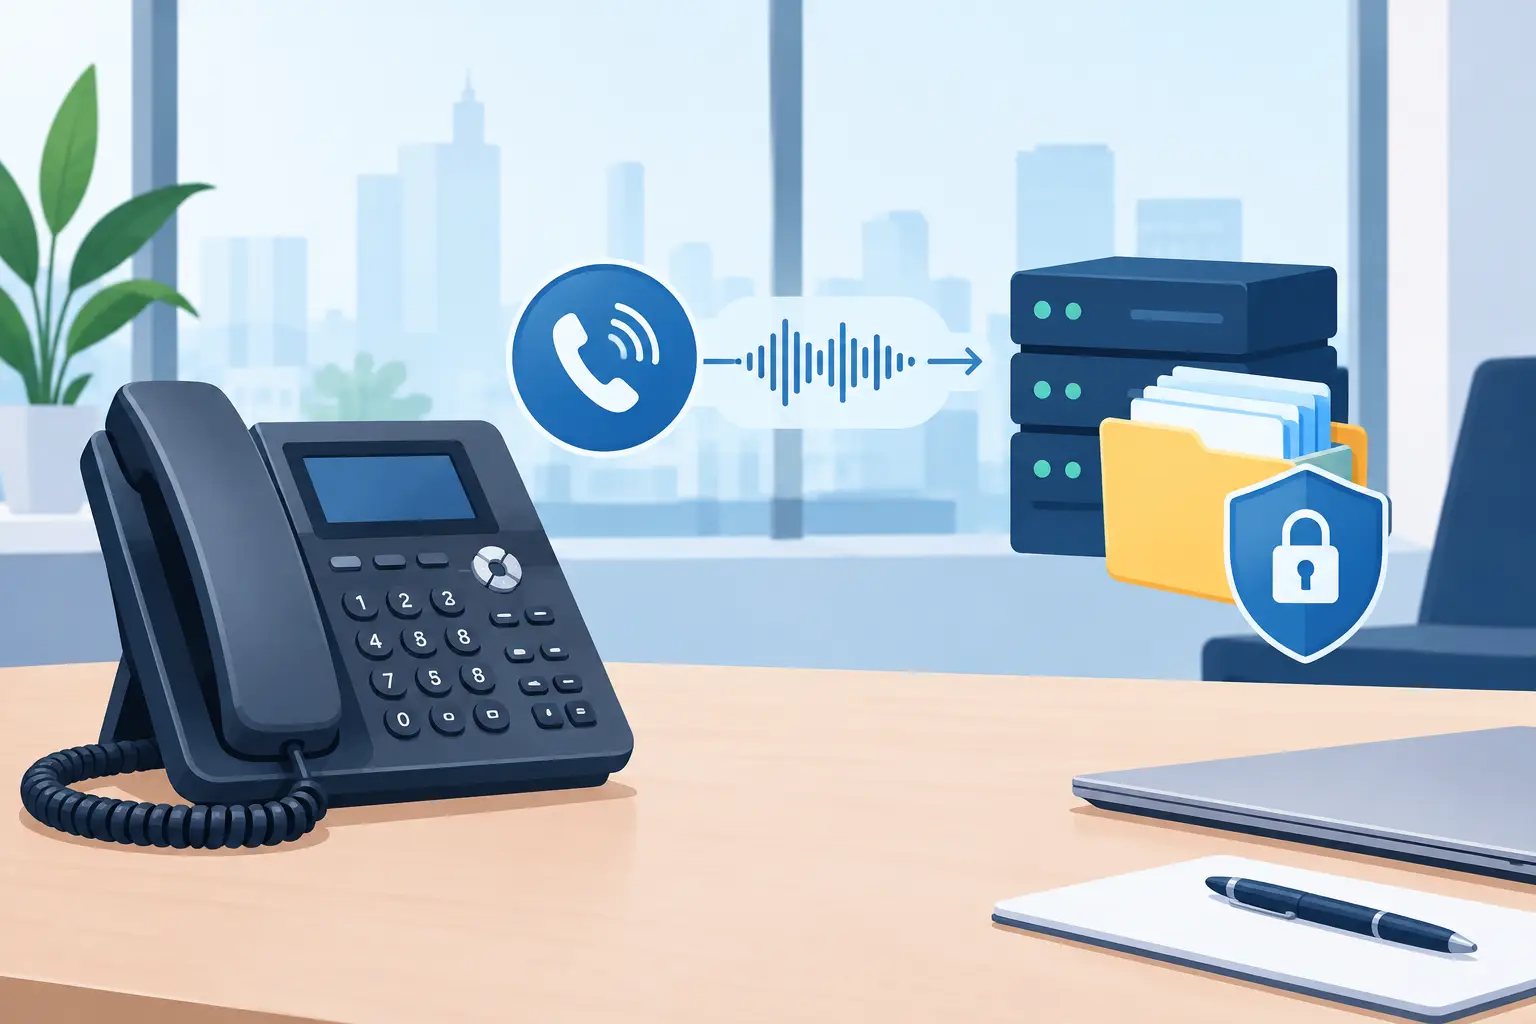
A recording that helps resolve a customer dispute on Tuesday can become an unnecessary security exposure six months later. That is the operational tension behind every effective call recording retention guide: retain recordings long enough to support service, compliance, training, and investigations, but not so long that storage, privacy, and legal risk accumulate without a purpose.
For contact centers and distributed business phone systems, retention is not simply a storage setting. It is a policy decision that affects customer experience, information security, regulatory readiness, and total cost of ownership. The right answer is rarely a single number applied to every call.
What call recording retention actually means
Call recording retention defines how long audio files, screen recordings, transcripts, metadata, and related interaction records remain available before they are deleted or archived. A complete policy also establishes who can access those records, where they are stored, how deletion is verified, and when normal deletion must stop because of a legal hold or active investigation.
The distinction between retention and backup matters. A backup may preserve a copy for disaster recovery, but it should not silently override the retention schedule. If an organization deletes a recording under policy while a secondary system keeps it indefinitely, the practical outcome is indefinite retention. That creates avoidable exposure and makes the policy difficult to defend.
Retention also applies to more than voice. Modern customer interactions may include voicemail, SMS, chat, email, social messaging, AI-generated summaries, and analytics data. If an agent can access or act on the information, it deserves a place in the organization’s records strategy.
Why one retention period rarely works
A sales qualification call, a payment-support call, and a regulated financial transaction do not carry the same business value or risk. Applying one blanket retention rule is easy to administer, but it can leave critical records unavailable while retaining lower-value content for too long.
Start with the purpose of each recording category. Quality assurance teams may need recent interactions for coaching and calibration. Operations teams may need calls long enough to investigate complaints, delivery disputes, or service failures. Compliance teams may require longer periods for certain regulated activities. Legal teams may need the ability to preserve targeted recordings when a dispute is anticipated or underway.
The governing requirements depend on industry, jurisdiction, contract obligations, and the subject matter of the call. US consent requirements also vary by state, particularly where parties to a call are located in different states. A retention schedule should be reviewed with qualified legal and compliance stakeholders rather than copied from another company’s policy.
Build a defensible call recording retention policy
A defensible policy connects each retention period to a documented business reason. It should be specific enough for administrators to configure and auditors to evaluate, without becoming so complicated that teams cannot follow it.
Classify recordings by purpose and sensitivity
Begin by mapping the interaction types your organization records. Typical categories include customer service, sales, collections, technical support, regulated transactions, internal meetings, and emergency or incident-related calls. Then identify what each category may contain: personal information, account details, health information, payment card data, trade secrets, authentication details, or employee information.
This exercise often reveals that some interactions should not be recorded in full at all. For example, payment information should be paused, masked, or handled through a secure payment workflow rather than captured in an agent recording. The strongest retention strategy reduces unnecessary collection before it tries to manage deletion later.
Define a business owner for every category
IT should administer the platform, but IT should not be the only owner of retention decisions. Assign accountable business owners across customer experience, operations, compliance, legal, security, and records management. Each owner should confirm why a category is recorded, who requires access, how long the content remains useful, and what event triggers disposal.
This prevents a familiar failure mode: recordings remain available because no one feels authorized to remove them. Retention is an active lifecycle process, not a default setting left untouched after deployment.
Use event-based rules where they add value
A fixed period from the call date is appropriate for many routine interactions. In other cases, an event-based trigger is more accurate. A complaint-related call may need to remain available until the complaint closes plus a defined period. A contract-support conversation may follow the lifecycle of the customer agreement. A recording subject to a legal hold must remain preserved until the hold is formally released.
Avoid creating dozens of exceptions unless the platform can reliably automate them. A simpler schedule that is consistently enforced is more defensible than a highly detailed schedule maintained through manual workarounds.
Set retention periods with risk, value, and cost in view
There is no universal number of days or years that fits every organization. The practical question is whether the ongoing value of a recording justifies the security, privacy, and storage burden of keeping it.
For routine quality assurance, teams commonly need a relatively recent sample of calls rather than a permanent archive. For dispute resolution, the useful period may align with refund windows, contract terms, or customer complaint processes. Regulated interaction types may require a different schedule based on applicable rules and documented advice from counsel.
Storage cost should be evaluated honestly, but it should not be the sole driver. Lower-cost archive tiers can help preserve records that must be retained while reducing the expense of primary storage. However, archive access controls, searchability, encryption, and deletion controls still need to meet the same security standard. Cheap storage is not a reason to keep sensitive recordings forever.
Secure recordings throughout their lifecycle
Retention without access governance is incomplete. Call recordings often contain enough context to support social engineering, identity theft, commercial disputes, or employee privacy claims. Security controls should reflect that reality.
At a minimum, recordings should be encrypted in transit and at rest, with role-based access that limits playback, download, deletion, and export permissions. Supervisors may need access to their teams’ interactions, while compliance personnel may require broader review authority. Those roles should not automatically include unrestricted download rights.
Maintain audit logs for access, playback, export, deletion, and policy changes. Logs are essential when investigating misuse or demonstrating that controls worked as intended. Multi-factor authentication, session controls, and centralized identity management further reduce the risk of recordings being exposed through compromised credentials.
For organizations with strict data residency, isolation, or infrastructure requirements, deployment architecture also matters. A platform that supports cloud, private, self-hosted, or dedicated environments gives IT leaders more control over where recordings and associated metadata reside.
Automate deletion, but preserve legal holds
Manual deletion is unreliable at scale. The retention engine should automatically delete or securely purge recordings when their retention period expires. Administrators need reports that confirm deletion jobs completed and identify any records excluded from disposal.
Legal holds are the critical exception. When legal, compliance, or investigation teams identify relevant interactions, the system must suspend ordinary deletion for the defined records. The hold should be targeted, documented, access-controlled, and reviewed periodically. An indefinite hold on broad populations of recordings can become another form of unmanaged retention.
A useful control is a release workflow: only authorized personnel can remove a hold, and the action is logged. Once released, the affected recordings should return to the applicable retention schedule rather than remain permanently preserved by accident.
Test the policy against real operating conditions
A retention policy is only credible when it works during ordinary operations and high-pressure events. Test whether an authorized supervisor can find a recent interaction, whether a restricted user is blocked from exporting it, whether a legal hold prevents deletion, and whether expired recordings are removed from every relevant storage location.
Include transcripts, AI summaries, CRM attachments, and analytics exports in these tests. A recording may be deleted correctly while a transcript or interaction summary remains in another system with no aligned retention rule. That gap is especially common as contact centers add AI-powered quality management and customer experience automation.
Review the policy at least annually and whenever the business enters a new market, launches a new communication channel, adopts a new integration, or changes its recording practices. Changes in call flows can introduce new sensitive data long before a written policy catches up.
Make retention a platform capability, not a cleanup project
The most efficient programs configure retention at the interaction level from the beginning. RingQ customers can align recording controls with communication workflows, user roles, and deployment requirements instead of relying on disconnected exports and periodic cleanup exercises.
That approach gives operations teams reliable access to the interactions they need while giving IT and compliance teams a clearer enforcement model. The goal is not to keep every conversation. It is to keep the right record, for the right reason, for exactly as long as the organization can justify it.
See RingQ in action
Talk to our team and find the right cloud PBX and contact center setup for your business.
Book a demo