
RingQ Security Patch: Critical PHP Vulnerabilities (October 2026)
RingQ now ships patched PHP for both new and existing systems. New installs and the RingQ Docker image include the fixed PHP from day one, and existing servers patch themselves the next time you press Update.
RingQ now ships patched PHP for both new and existing systems. New installs and the RingQ Docker image include the fixed PHP from day one, and existing servers patch themselves the next time you press Update.
On 21 October 2026, the PHP project disclosed two critical vulnerabilities, CVE-2026-109618 and CVE-2026-109619. The US Cybersecurity and Infrastructure Security Agency (CISA) followed with an alert urging immediate patching. The RingQ web portal and management services run on PHP, so we treated this as urgent and had fixes out within two days.
Both flaws let an attacker run their own code on a web server that uses PHP, without logging in. A single crafted web request can be enough, and working exploit code is already public.
- CVE-2026-109618 (CVSS 9.2): memory corruption when PHP runs out of memory while it reads a request, for example a large file upload.
- CVE-2026-109619 (CVSS 9.2): data left over from a failed request can be reused by the next request on the same PHP worker.
Every PHP version from PHP 5 onward is affected. The PHP project fixed them in 8.5.12, 8.4.27, 8.3.36 and 8.2.35, and backported fixes to older branches through Linux distribution and repository maintainers (CERT-EU advisory).
How we patched RingQ, for new and existing systems
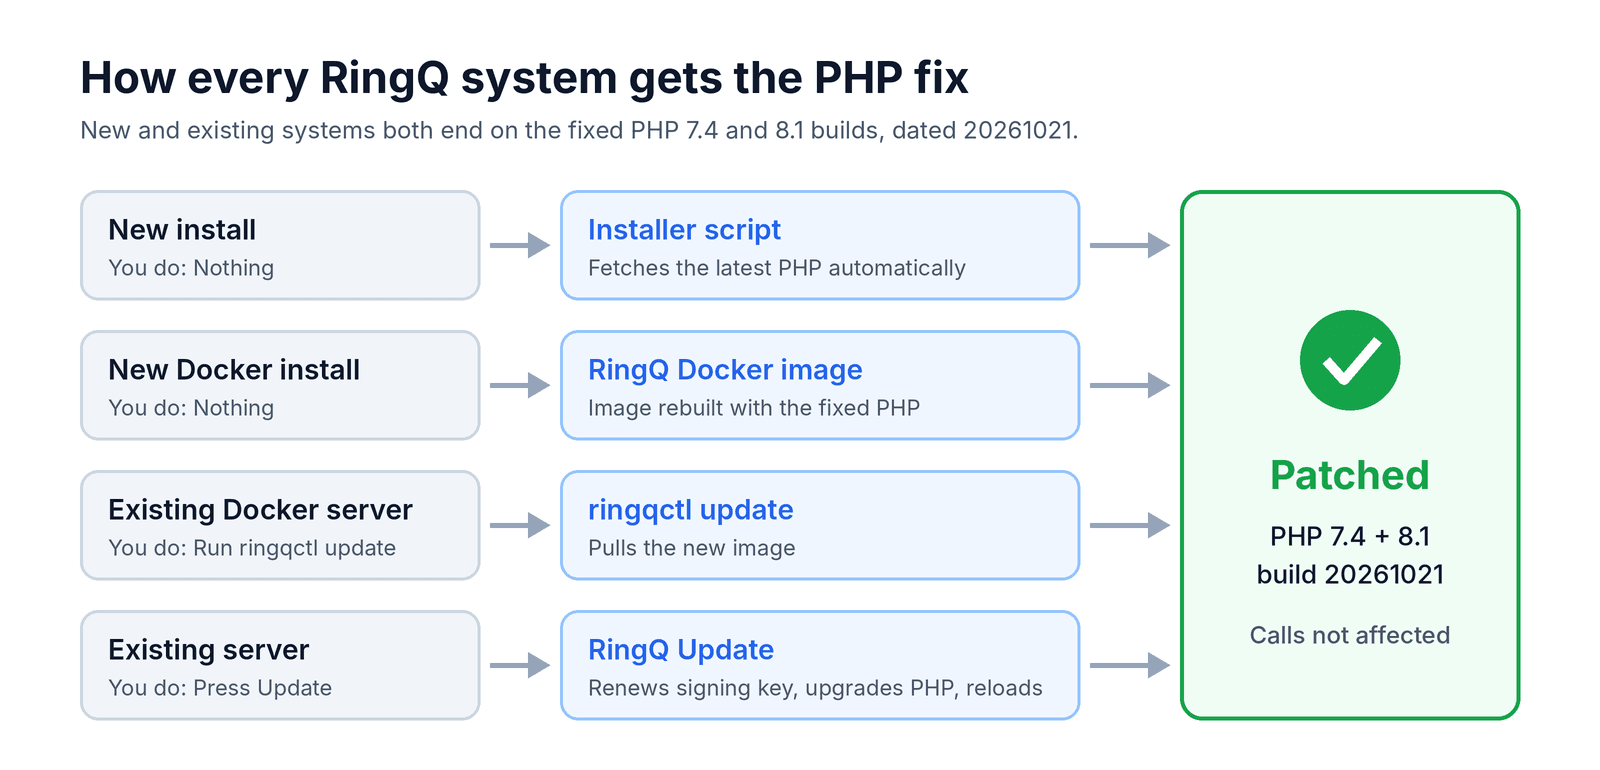
RingQ uses PHP 7.4 and PHP 8.1. Our PHP package provider published fixed builds of both on 21 October 2026. We rolled them into every way RingQ gets onto a server:
| System | How it gets the fix | What you do |
|---|---|---|
| New installs (installer script) | The installer always fetches the latest PHP packages, so a fresh install gets the fixed builds automatically. | Nothing |
| New Docker installs | We rebuilt the RingQ Docker image with the fixed PHP 7.4 and 8.1 builds and verified the versions before release. | Nothing |
| Existing Docker servers | Updating pulls the new image, which already has the fixed PHP. | Run ringqctl update |
| Existing servers (installed with the script) | The RingQ Update now checks the PHP version. If it is older than the fix, it upgrades only the PHP packages and reloads PHP. It also renews the package signing key on older servers, so they can download the fix. | Press Update in the RingQ portal |
The RingQ Update also applies the PHP Foundation's recommended safeguard: PHP's upload-progress tracking is switched off. RingQ does not use it, and turning it off closes one of the attack paths.
The upgrade stays on the same PHP versions RingQ already uses, so the RingQ portal, apps and licensing keep working as before. Calls are not interrupted: the update restarts only the web services, and calls run on separate RingQ Call Services. The web portal may pause for about a second while PHP restarts.
What you need to do
- RingQ-hosted systems: our team is rolling the update out. You don't need to do anything.
- Self-hosted RingQ: log in to the RingQ portal as an administrator and press Update. The PHP fix runs as part of the update and takes a few minutes.
- Self-hosted RingQ on Docker: run ringqctl update on the server to move to the new image.
Please update as soon as you can. Exploit code is public, and any RingQ server reachable from the internet should be treated as at risk until it is updated.
If you can't update straight away, limit access to the RingQ web portal with a firewall or VPN until you can. If other PHP applications run on the same server, patch those too.
Check that you're patched
On the server, run dpkg -l php7.4-fpm php8.1-fpm. Both version strings should contain a build date of 20261021 or later, for example 7.4.33-31+0~20261021.121 and 8.1.34-9+0~20261021.82. On Docker, run the same command inside the RingQ container.
If the version is still older after updating, or you'd like help, contact RingQ support and we'll patch the server with you.
Our commitment to security
At RingQ, we are ISO 27001 and HIPAA compliant, so we take security very seriously. We watch for new vulnerabilities in everything RingQ runs on, test fixes on our own systems first, and ship them to customers as quickly as we safely can.